
At AEON TECH SOLUTION INC., we help organizations strengthen their IT security, protect sensitive information, manage technology risks, and establish practical security controls that support business and compliance requirements.
Our IT Security & Compliance Services combine cybersecurity, risk management, identity protection, security monitoring, policy development, employee awareness, and compliance assessments. We work with organizations to identify security gaps, improve their security posture, and establish a structured approach to protecting systems, data, users, and business operations.
Whether you are a small business looking to establish a security foundation or an enterprise organization requiring ongoing security management, AEON TECH can help develop a security program aligned with your environment and business objectives.
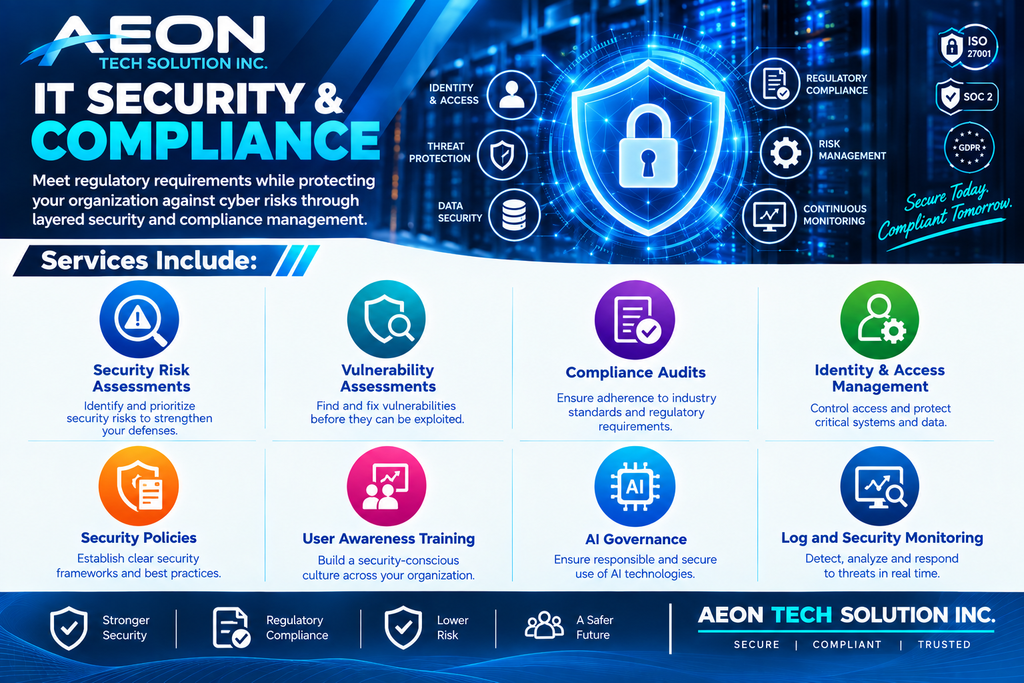
Our IT Security & Compliance Services Include
1. Security Risk Assessments
We evaluate your IT environment to identify potential security risks and areas requiring improvement.
Our assessments can review:
- Servers and infrastructure
- Network architecture
- Firewalls
- Endpoints
- Cloud services
- User accounts
- Administrative access
- Remote access
- Data protection
- Backup infrastructure
- Security controls
- Existing policies and procedures
We document identified risks and provide practical recommendations that can be prioritized according to business impact and security requirements.
2. Vulnerability Assessments
We help identify weaknesses in systems, applications, infrastructure, and configurations that could potentially be exploited.
Our vulnerability assessment services can include:
- Server vulnerability reviews
- Endpoint assessments
- Network device assessments
- Firewall configuration reviews
- Cloud configuration reviews
- Application assessments
- Missing security updates
- Weak configurations
- Exposed services
- Risk prioritization
The objective is to help organizations understand where vulnerabilities exist and determine appropriate remediation actions.
3. Compliance Audits
Organizations may need to meet specific regulatory, contractual, industry, or customer security requirements.
We help review existing security controls and identify gaps against applicable requirements.
Compliance-related assessments may consider areas such as:
- Data protection
- Access control
- Password and authentication requirements
- Security monitoring
- Logging
- Backup and recovery
- Incident response
- Security policies
- Employee awareness
- Vendor management
- Risk management
We provide documentation and recommendations to help organizations improve their compliance readiness.
4. Identity & Access Management
Controlling who can access systems and information is a fundamental component of IT security.
We help organizations implement and manage:
- User account controls
- Role-based access
- Least-privilege access
- Multi-factor authentication
- Single sign-on
- Conditional access
- Privileged accounts
- Administrative access
- Access reviews
- User onboarding and offboarding
Our goal is to ensure users have the appropriate access required to perform their responsibilities while reducing unnecessary exposure.
5. Multi-Factor Authentication
Passwords alone may not provide sufficient protection for business systems.
We help implement MFA for:
- Microsoft 365
- Cloud applications
- VPN
- Remote access
- Administrative accounts
- Critical business applications
- Privileged access
MFA adds an additional authentication factor and can help reduce the impact of compromised credentials.
6. Security Policies & Procedures
Technology controls are most effective when supported by clear policies and procedures.
We help organizations develop and review policies covering areas such as:
- Acceptable technology use
- Password management
- MFA
- Remote access
- Data protection
- Mobile devices
- Email security
- Internet usage
- Access control
- Incident response
- Backup and recovery
- Employee security responsibilities
- Third-party/vendor security
Policies can be structured according to the organization’s size, operational requirements, and applicable compliance obligations.
7. User Security Awareness Training
Employees play an important role in protecting an organization’s technology environment.
We provide security awareness programs covering topics such as:
- Phishing
- Social engineering
- Password security
- MFA
- Suspicious emails
- Malicious attachments
- Safe web browsing
- Data protection
- Remote work security
- Physical security
- Incident reporting
Security awareness helps employees recognize common threats and understand their responsibilities when handling company systems and information.
8. AI Governance & Security
As organizations increasingly adopt artificial intelligence, new security, privacy, and governance considerations need to be addressed.
We can help organizations establish practical AI governance controls covering:
- Approved AI tools
- Acceptable AI usage
- Sensitive data handling
- Confidential information
- Access controls
- Third-party AI services
- AI-related risks
- Employee guidelines
- Data privacy considerations
- Security review processes
The goal is to allow organizations to benefit from AI while establishing appropriate controls around its use.
9. Log & Security Monitoring
Security monitoring provides visibility into activities occurring throughout your IT environment.
We help organizations monitor relevant security events from:
- Servers
- Firewalls
- Network devices
- Endpoints
- Cloud platforms
- Identity systems
- Applications
- Security tools
Monitoring can help identify unusual authentication activity, suspicious system changes, unauthorized access attempts, malware events, and other security-related activities.
10. Security Reporting
Security information needs to be understandable and actionable.
We can provide reporting around:
- Security events
- Vulnerabilities
- Patch status
- Endpoint security
- Firewall activity
- User access
- Authentication events
- Backup status
- Security incidents
- Compliance gaps
- Recommended remediation
Reports can provide management with greater visibility into the organization’s overall security posture.
Additional IT Security Services
Endpoint Security
We help protect desktops, laptops, and servers through appropriate endpoint security technologies and controls.
Services can include:
- Endpoint protection
- EDR/MDR
- Malware protection
- Device controls
- Security policies
- Endpoint monitoring
- Security configuration
- Patch management
Network Security
We help protect network infrastructure through:
- Firewall implementation
- Network segmentation
- Secure VPN
- Intrusion detection and prevention
- Wireless security
- Network access controls
- Secure remote access
- Network monitoring
Email Security
We help protect business email against common threats such as:
- Phishing
- Malware
- Malicious attachments
- Spoofing
- Business email compromise
- Spam
- Unauthorized forwarding
- Suspicious links
Security Incident Response
When a security incident occurs, a structured response can help limit its impact.
We can assist with:
Identify → Contain → Investigate → Remediate → Recover → Review
Services may include incident investigation, containment, system recovery, security review, and recommendations to reduce the likelihood of similar incidents.
Security Hardening
We review infrastructure configurations and implement appropriate security improvements.
Hardening may include:
- Removing unnecessary services
- Restricting administrative access
- Strengthening authentication
- Applying security updates
- Reviewing firewall rules
- Improving endpoint configurations
- Restricting network access
- Improving logging and monitoring
Compliance & Security Framework Alignment
Depending on your organization’s requirements, we can help assess security practices against recognized frameworks and standards such as:
- NIST Cybersecurity Framework
- ISO/IEC 27001
- CIS Controls
- SOC 2-related security controls
- Applicable privacy and contractual requirements
The specific requirements applicable to an organization depend on its industry, location, customers, services, and the type of information it handles.
Our IT Security & Compliance Approach
Assess → Identify → Protect → Monitor → Respond → Improve
Assess
Evaluate your current infrastructure, security controls, policies, and risks.
Identify
Determine vulnerabilities, security gaps, compliance requirements, and areas requiring attention.
Protect
Implement appropriate security controls, policies, access management, and technical protections.
Monitor
Continuously monitor systems and security events to improve visibility.
Respond
Establish procedures for investigating and responding to security incidents.
Improve
Regularly review security controls and continuously improve your security program.
Benefits of IT Security & Compliance Services
Reduced Security Risk
Identify weaknesses and implement appropriate controls to reduce exposure.
Improved Visibility
Gain greater insight into users, devices, systems, security events, and vulnerabilities.
Stronger Access Control
Ensure users receive appropriate access to business systems and information.
Better Security Awareness
Help employees recognize and respond appropriately to common cyber threats.
Improved Compliance Readiness
Identify security and documentation gaps that may affect regulatory, contractual, or customer requirements.
Stronger Business Resilience
Integrate security, backup, disaster recovery, and incident response into your overall IT strategy.
Ongoing Security Improvement
Security is not a one-time project. Regular assessments, monitoring, and reviews help organizations adapt as technology and threats change.
Why Choose AEON TECH SOLUTION INC.?
With more than 30 years of experience across IT infrastructure, servers, networks, firewalls, cybersecurity, cloud, automation, and business continuity, AEON TECH takes a practical, infrastructure-focused approach to security.
We understand that cybersecurity and compliance must work together with your everyday IT operations. Our goal is to help organizations establish security controls that are practical, manageable, scalable, and aligned with their business requirements.
From security assessments and vulnerability management to identity protection, security monitoring, policies, employee awareness, and compliance preparation, AEON TECH can help build a stronger security foundation for your organization.
Secure Your Technology. Protect Your Data. Strengthen Your Business.
AEON TECH SOLUTION INC. — Practical IT Security & Compliance for a More Secure and Resilient Business.